[NEW!] Introducing AVA Agentic OS

CTEM Runs on AVA Agentic OS

AVA OS is the operating system for CTEM, orchestrating specialized AI agents that execute autonomous cybersecurity missions to continuously validate defenses, break attack paths, and reduce threat debt.

Request a Demo See AVA OS in Action

Every Assumption Is Now a Vulnerability

AI compresses the time between exposure and exploitation. Disconnected tools and point-in-time security assessments can’t keep pace.

AttackIQ defends at AI speed, turning threat intelligence, exposure data, and adversary emulation into a closed-loop system where findings drive validation and fixes become measurable progress.

You Don’t Catalog Assets.

You See Like
an Adversary

Map the assets, identities, and threats that shape your environment

You Don’t Chase Findings.

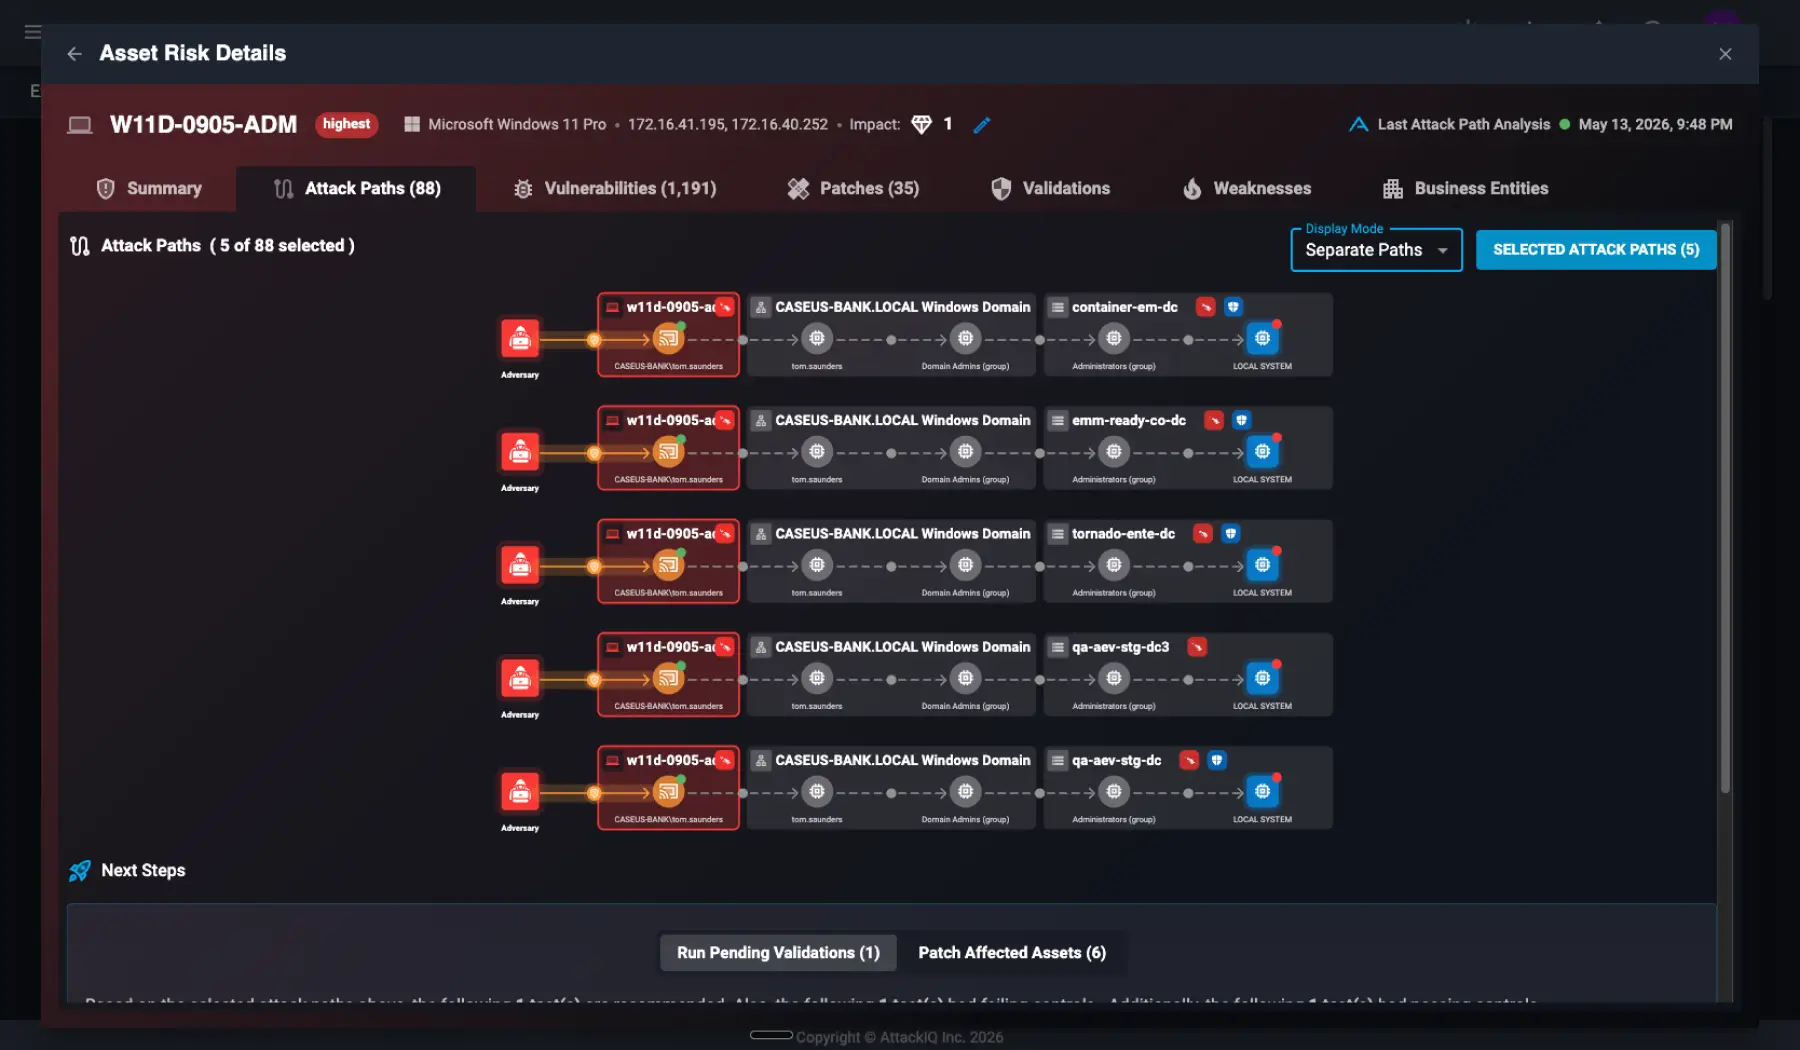
You Break Attack Paths

Pinpoint the exposures that create viable routes to critical systems

You Don’t Assume Coverage.

You Prove
It Works

Validate controls against the techniques adversaries actually use

You Don’t Report Activity.

You Reduce Threat Debt

Continuously break the attack paths that put your business at risk

Explore the CTEM Platform

Threat Debt Index

Prove Attacker Opportunity Is Going Down

The AttackIQ Threat Debt Index™ gives teams and leadership a single view of exploitable opportunity over time: current balance, what was reduced, and what has newly accrued as conditions changed.

It reports outcomes, not activity, so you can prove progress, not just claim it.
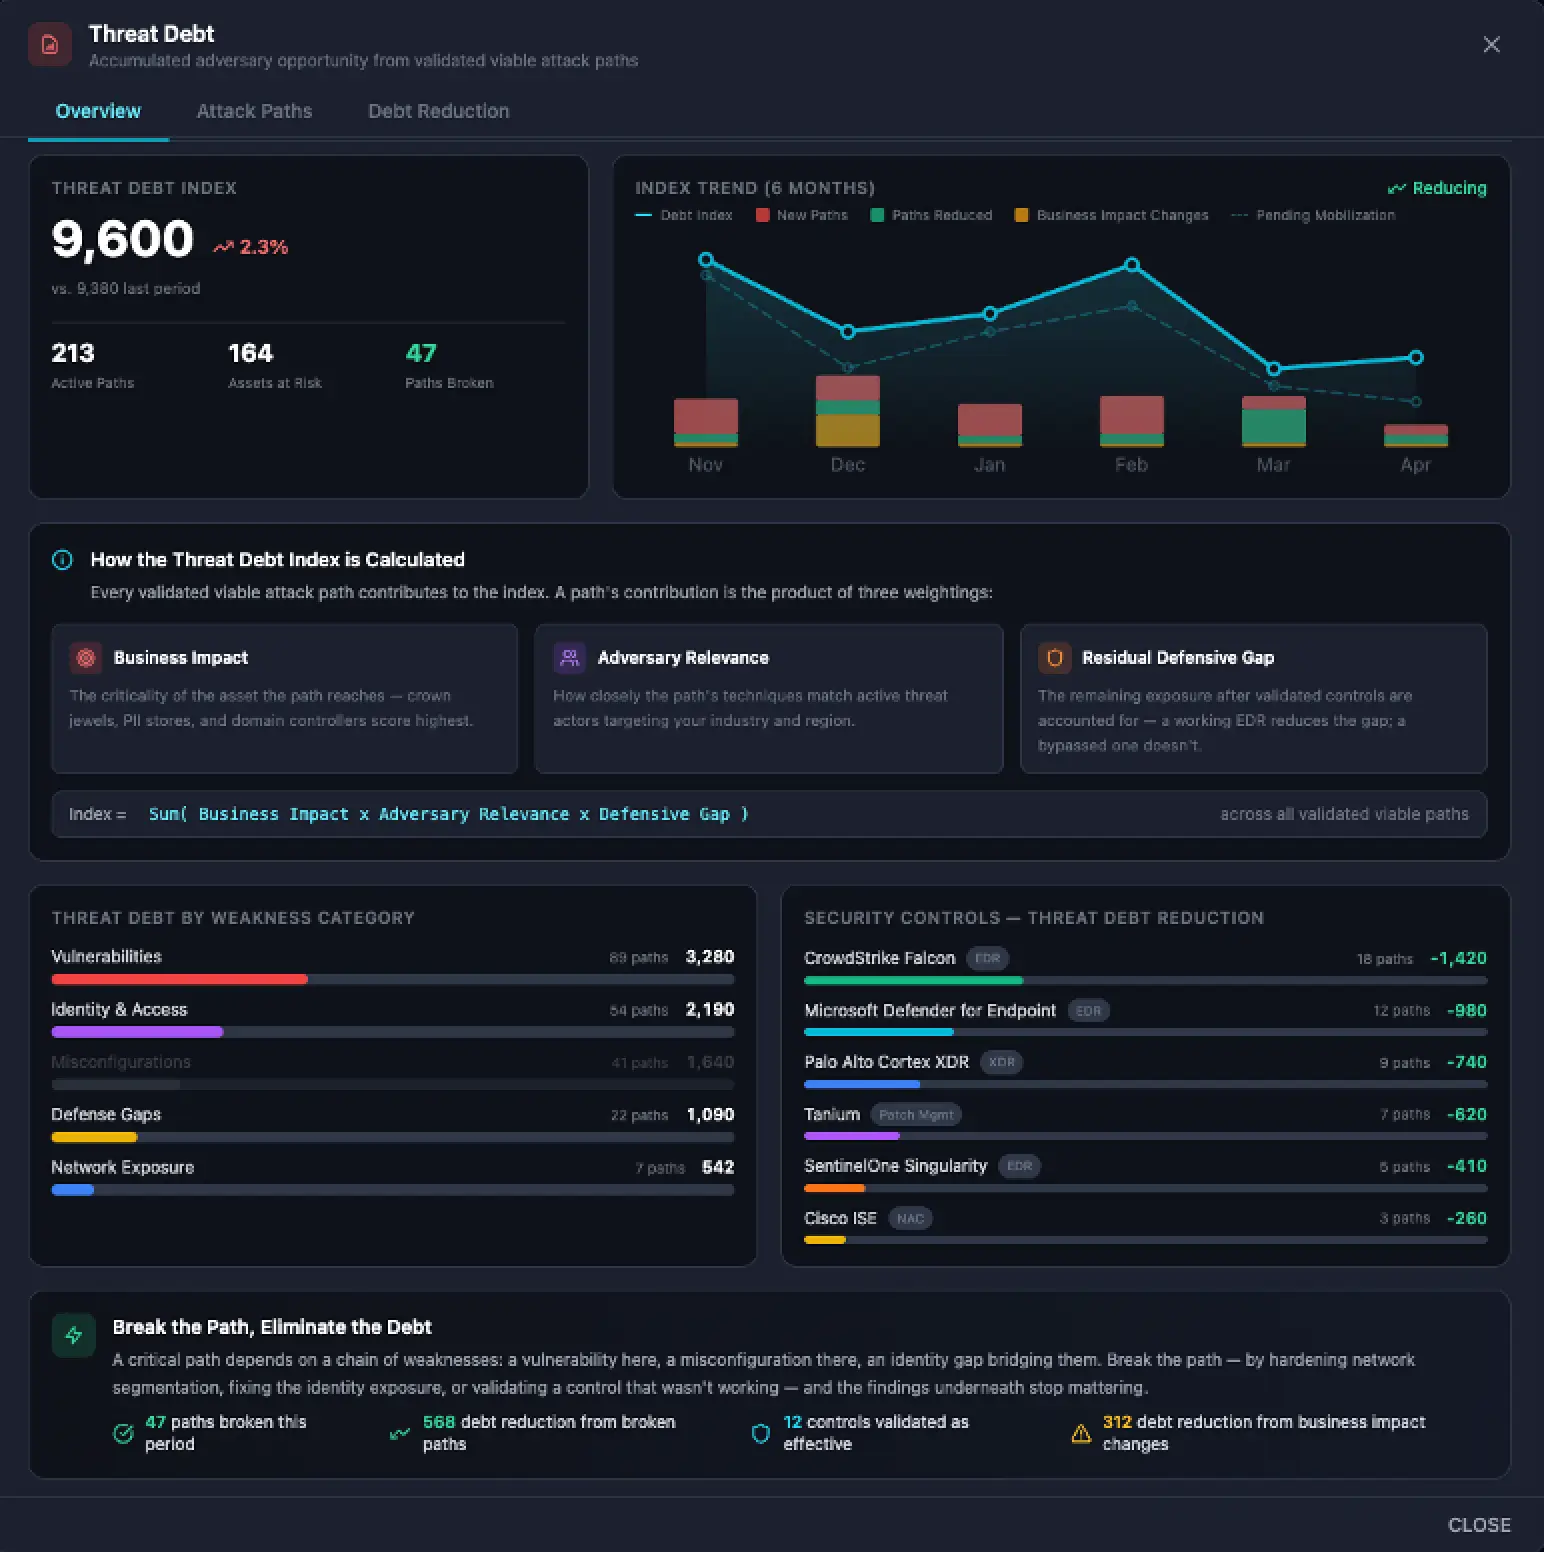
What Is Threat Debt?

Built for the Way CTEM Actually Works

CTEM is the framework. AttackIQ turns it into results you can measure.

Exposure Management

Not Every Exposure Creates Risk

Which ones actually put the business at risk?

Most exposure lists are ranked by severity, with noise. AttackIQ prioritizes based on attacker reach, business impact, and validated exploitability, so teams focus on the paths that pose meaningful risk
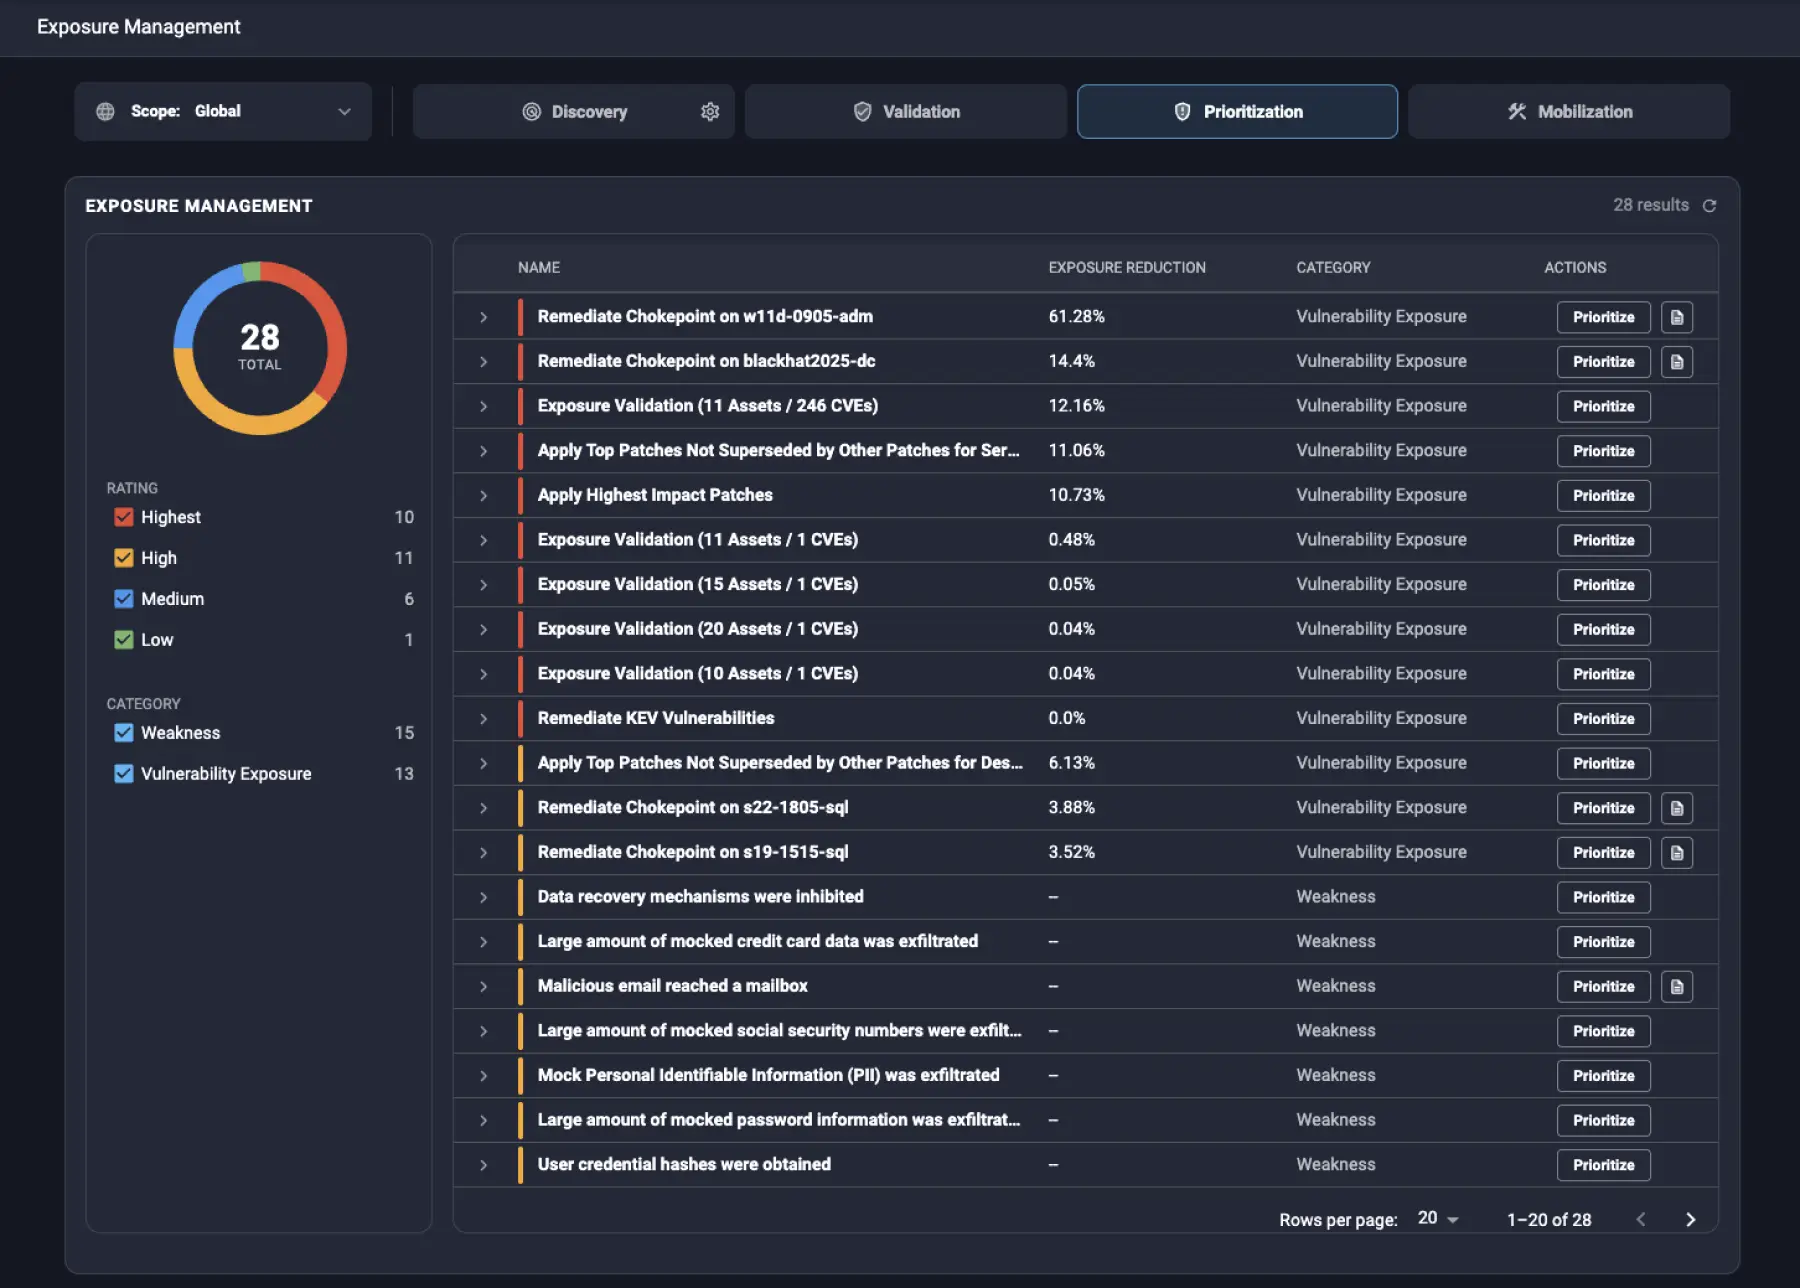
Reduce Exposure

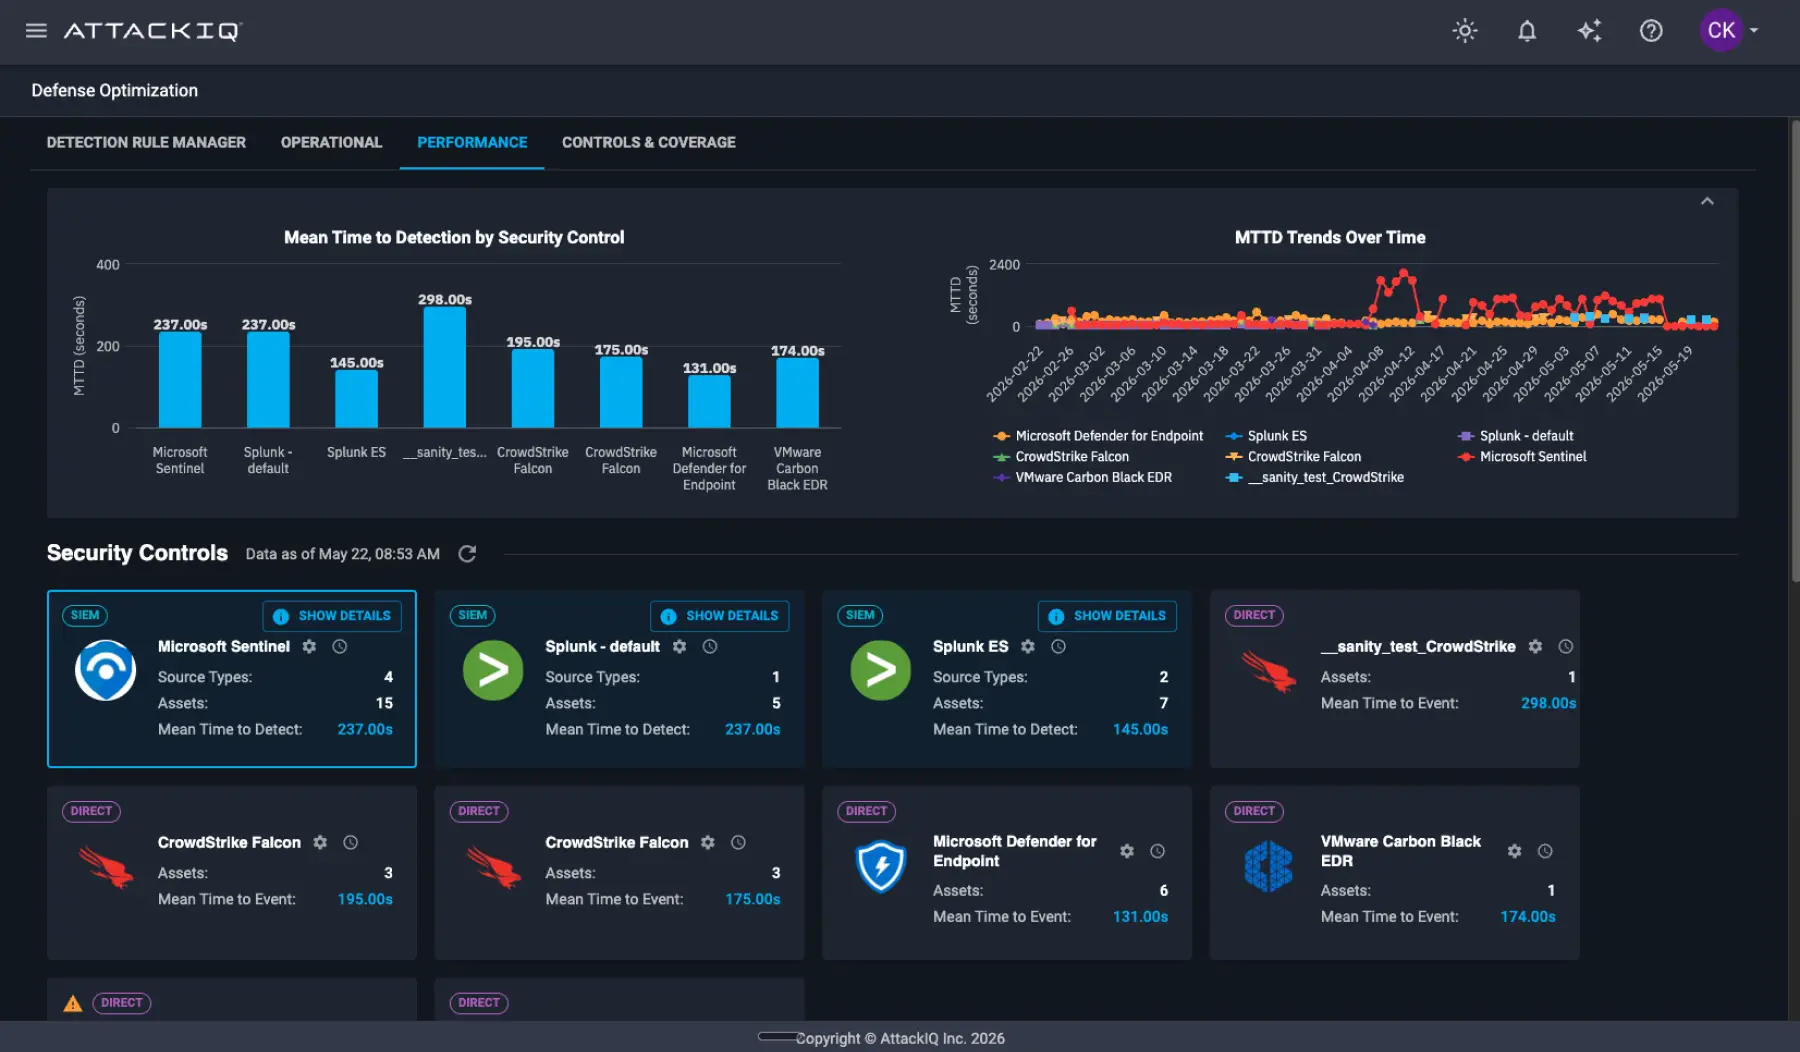
Detection Engineering

Your Detections Have Gaps

You just can’t see them yet

Map detection coverage to how attacks actually operate. Tune what adversaries exploit, not just what generates the most alerts

Improve Detection

Security Control Validation

Deployed Doesn’t Mean Effective

Are your controls stopping attacks or failing silently?

Validate whether controls block, detect, alert, and escalate against adversary techniques across your environment

Validate Controls

Offensive Testing

Point-In-Time Tests Don’t Hold

How do you know what still works?

Execute full attack paths across identity, cloud, endpoint, and network environments continuously, not occasionally

Run Offensive Testing

What CTEM Done Right Looks Like

Threat Debt Index

Pay Down Rate

Mean Time to Detect (MTTD)

45% Faster, in 90 Days

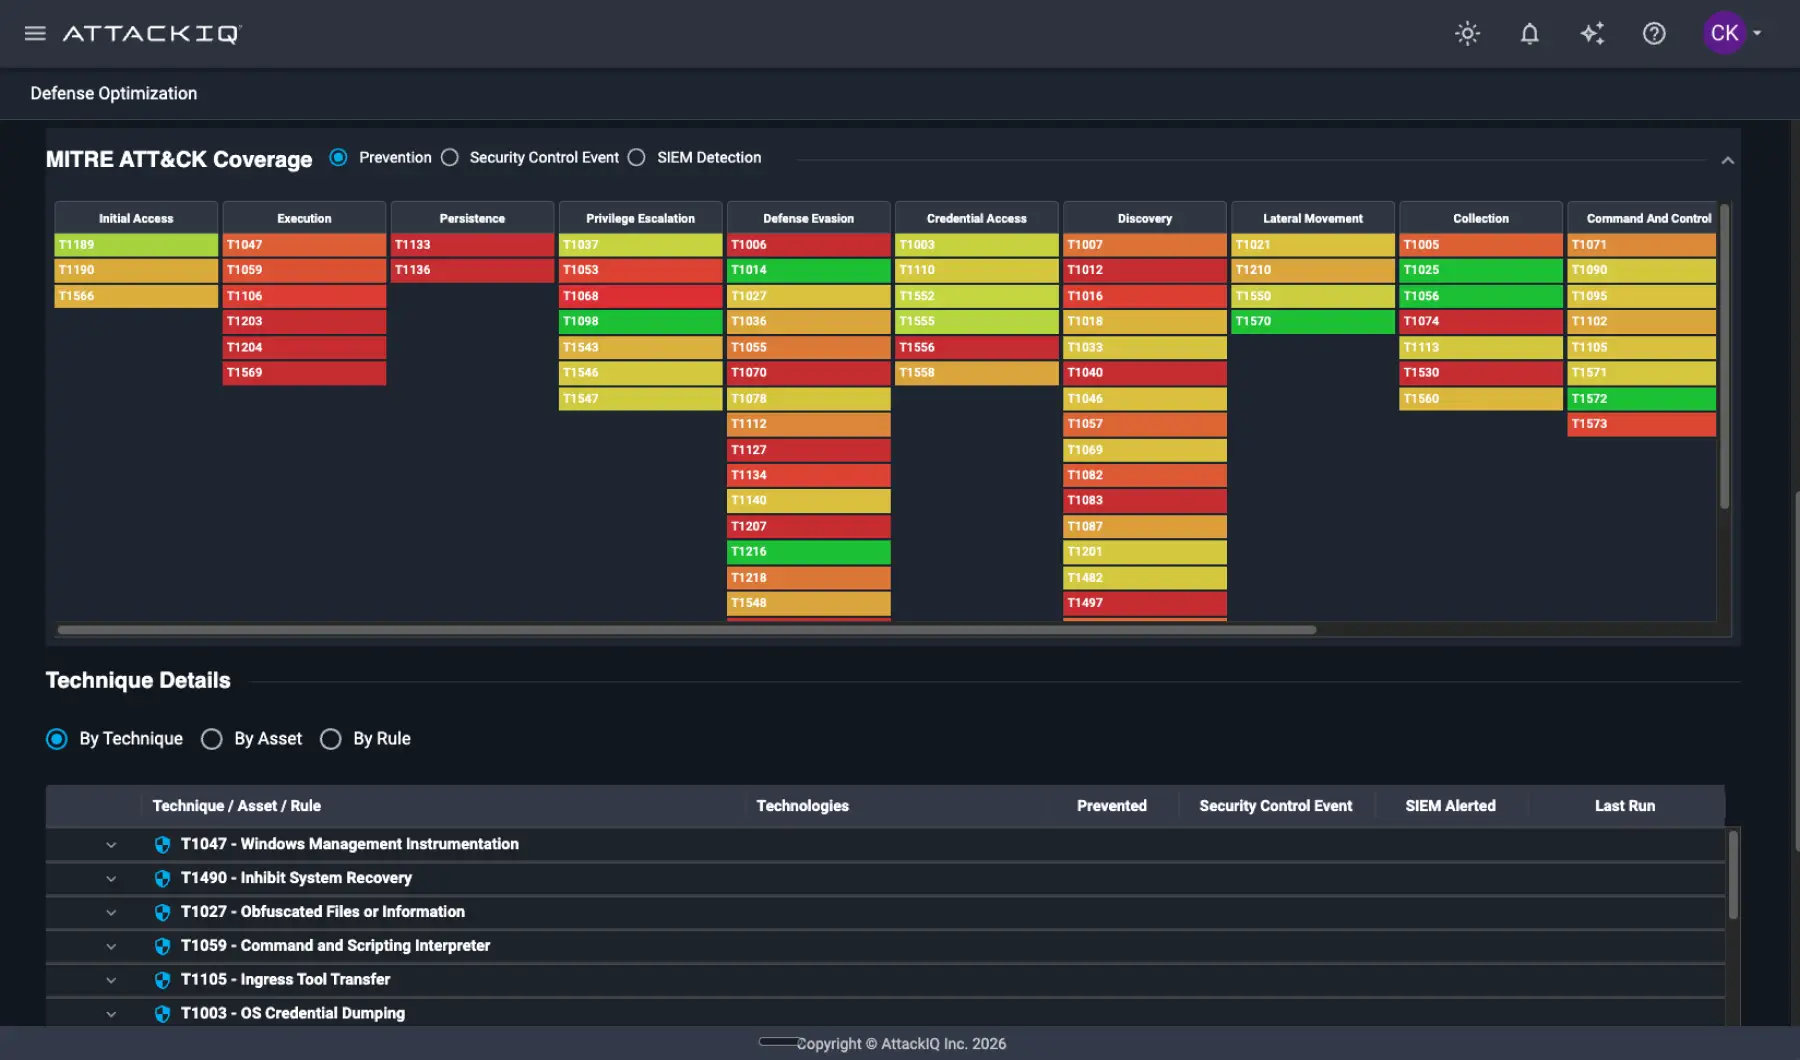
MITRE ATT&CK Coverage

Tested Against Techniques That Matter Most

Operationalize CTEM

CTEM In
90 Days

Go from scoping to mobilization, fully operational in 90 days.
Start CTEM in 90 Days

Smarter Security,
Proven Results

Gain unparalleled visibility, efficiency, and control for unmatched protection,
cost savings, and peace of mind.

0
Lower Breach Costs
0
Faster Security Operations
0
Higher SOC Analyst Output
0
Reduced Tool Sprawl

Real Impact for Real-World
Security Challenges

From Fortune 500 companies to mid-sized enterprises, organizations across industries trust us to keep them resilient.

  • Fortune 500 Asset Management Firm (Finance)

    “At first it was difficult to maintain the cadence of operations as people took to their home offices. However, with AttackIQ, we had a platform that could continue the same levels of automated testing regardless of what was going on around it. That helped us establish a strong baseline and understand what was happening to key controls during this chaotic period.”
    Red Team Leader
    Fortune 500 Asset Management Firm Empowers its Purple Team with the AttackIQ Security Optimization Platform
  • Energy

    “That’s what’s great about AttackIQ, it allows us to identify our biggest potential security control gaps and gives us the visibility we need to ensure our controls are up to scratch. The AttackIQ Security Optimization Platform is therefore a fundamental layer of our threat-informed defense.”
    Head of Cyber Security
    SA Power Networks, an Australian Energy Company, Improves Security Control Validation and Reduces Costs with AttackIQ
  • Insurance

    “They might think they’ve successfully closed a control gap. We can prove whether that’s true; we don’t have to take their word for it. Without AttackIQ, it would be possible for my team to do that, but it would be extremely time-consuming. They would have to reach out to the end user support team, get a machine on the network in question, then run the attack and see whether it succeeds. With Attack IQ, we just push a button to re-run the test that revealed the problem in the first place.”
    Director of Information Security
    Major General Insurer Boosts Cybersecurity Readiness Across a Broad and Diverse Infrastructure
  • Defense, Transportation

    “The reports are easy for management to understand; we do not get many questions about them. Also, the AttackIQ Security Optimization Platform enables us to run monthly scenarios emulating the latest threats showing up in the news. Because we understand, and can demonstrate, whether our systems and processes will prevent specific current threats, we can quickly communicate to our leadership what the risk level is.”
    Senior Information Security Analyst and Security Tester
    U.S. Defense Contractor Harnesses AttackIQ to Improve Customers’ Operational Readiness
  • Facility Management Services

    “It helps me provide detailed reports to the C-suite, the board, and auditors to create transparency around our return on investment as a corporate security function. There are still a lot of things that keep me up at night, but I am sleeping much better now than I did before we started working with AttackIQ.”
    Chief Information Security Officer (CISO)
    ISS World Services A/S, One of the World’s Leading Facilities Management Providers, Finds Efficient Road to Security Visibility
  • Retail

    “One of our goals is to run standard tests across all the environments and regions we operate in. We want to know that all our stores have the same security, regardless of where they’re located. “Because testing in the Security Optimization Platform is programmatic, the tests are done in the same way on every system in every country, on every continent. If I run the test today, next week, and then again four years from now, the results will be comparable, apples to apples, unless we have purposely changed something. The Security Optimization Platform doesn’t just enable us to execute at scale; it also enables us to execute consistently at scale, which is something we couldn’t do without underlying technology.”
    Director of Security Operations
    Building Confidence in Security Effectiveness Across a Fortune 500 Retailer’s Complex Global Infrastructure
  • Energy

    “AttackIQ gives us the ability to assess against our key threats, and that gives me the information I need to report to key stakeholders, such as the CIO or operations leads, that we are as secure as can be expected. Essentially, AttackIQ gives me the information I need to say with confidence that the programs and reporting we have in place are working to lower our cyber risk.”

    Head of Cyber Security
    SA Power Networks, an Australian Energy Company, Improves Security Control Validation and Reduces Costs with AttackIQ
  • Banking

    5 Star Review Overall experience with the product is great! The product has provided so much insight into our systems and has allowed improvement of overall security posture. Product can be in the high end in terms of pricing but it is money well spent! Regular updates of the attack library and the ability to customize it to your needs. Very simple to use.

    Information Security Specialist
    Gartner Peer Insights
  • Insurance

    “After an aquisition, we immediately work to build visibility into their security systems and processes, we make sure their teams understand our standards for setting up a defensible architecture, and then we validate that they are following through.” He adds, “For companies doing M&As, it doesn’t make any sense to not use a technology like AttackIQ.”

    Director of Information Security
    Major General Insurer Boosts Cybersecurity Readiness Across a Broad and Diverse Infrastructure
  • Security

    “When we use AttackIQ for training, we achieve greater visibility into our own cyber hygiene and countermeasures. That helps us further apply threat-informed defense internally, especially as adversary tradecraft evolves.”

    Managing Director
    The Chertoff Group Leverages AttackIQ Security Optimization Platform to Deliver Compelling Security Service for Clients
  • Biosciences

    “We have a good way to go with the maturity of the AttackIQ platform. Being a relatively small team, we still need to balance out our red, blue, and purple team exercises with daily operation responsibilities. But it is the platform we leverage for a better understanding of the network and overall security posture. AttackIQ provides supporting documentation and evidence that we are doing what we say we are.”

    Director of IT Security
    Leading Biosciences Company Demonstrates Security Control Effectiveness and Reduces Insurance Premiums Using AttackIQ
  • Insurance

    “Security teams that aren’t doing any control validation — any breach and attack simulation — have a serious gap in their visibility. Companies like ours, where different business units have different controls in place and maybe different security technologies, need insights into where each organization stacks up. Breach and attack simulation software is a good way to ensure that you’re well-positioned to respond to an actual attack.”

    Director of Information Security
    Major General Insurer Boosts Cybersecurity Readiness Across a Broad and Diverse Infrastructure

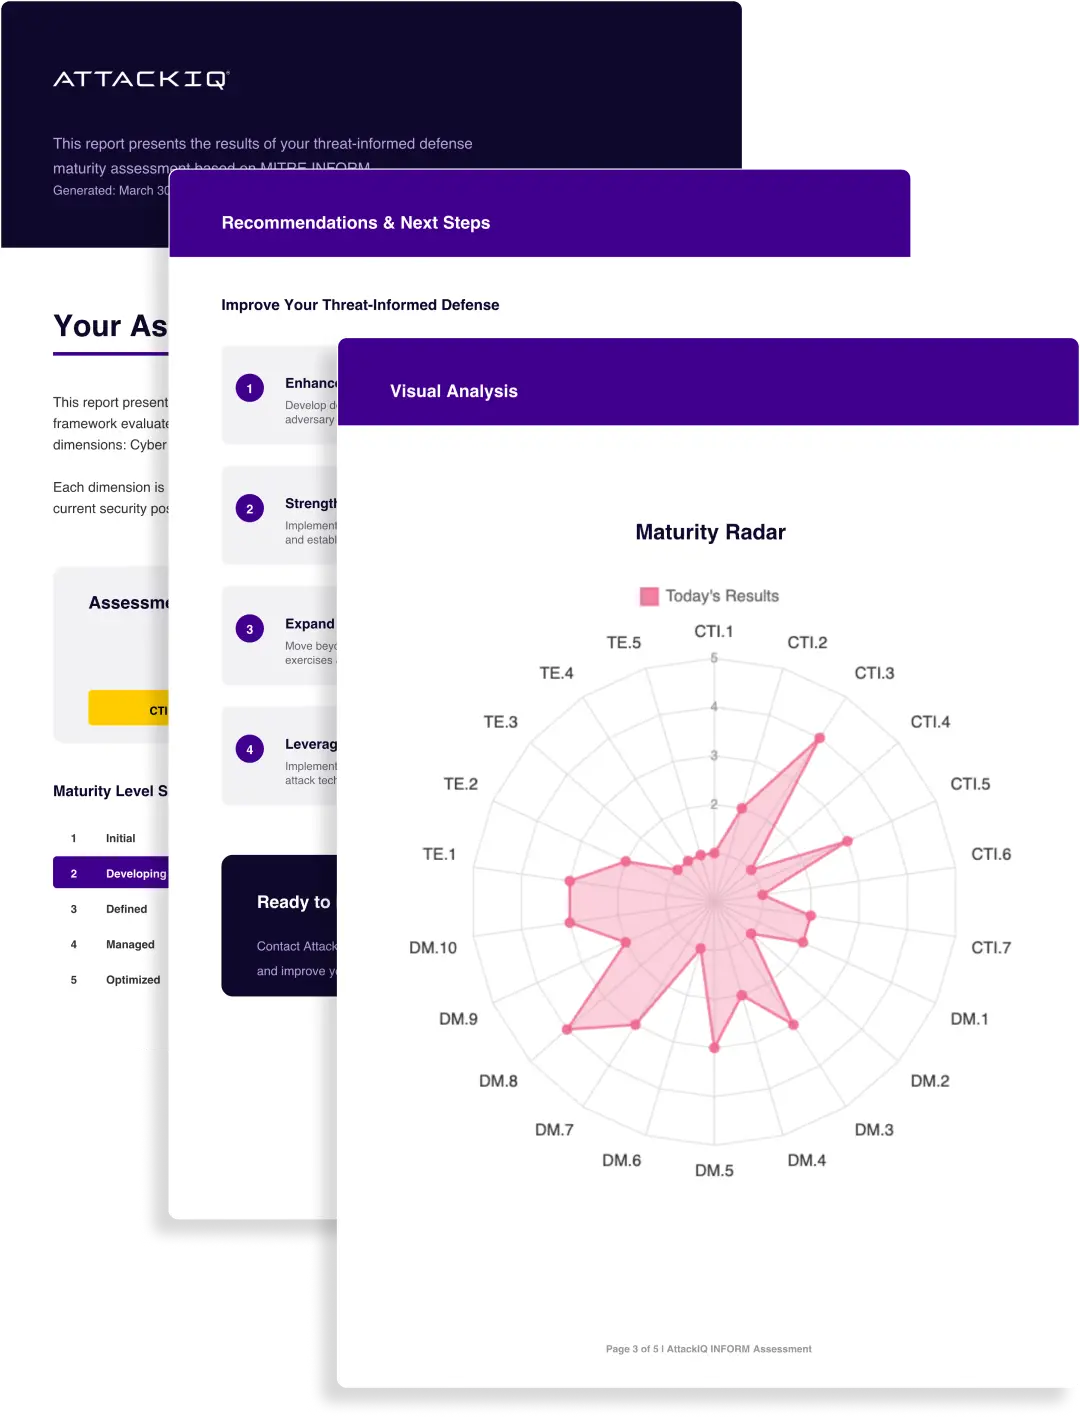
How Threat-Informed Is Your Defense, Really?

MITRE ATT&CK tells you how attackers operate. This tells you if your program is ready.

Benchmark your defense in minutes. Get a scored breakdown across CTI, Defensive Measures, Testing, and CTEM — with prioritized recommendations so you know what to fix first.
Take the Free Assessment

Featured Articles

  • CTEM + MITRE INFORM For Dummies

    This new For Dummies guide explains how Continuous Threat Exposure Management (CTEM) and MITRE INFORM work together to establish a continuous, measurable approach to cyber resilience, grounded in operational performance and real-world evidence.
    Read More
  • The AI Vulnerability Storm

    Anthropic reveals AI that autonomously discovers and exploits vulnerabilities at scale. This shift reshapes cyber risk—learn what it means and what to do.
    Read More
  • Threat Debt: The Unit of Measure Adversaries Already Use Against You

    Threat debt measures the exploitable attack paths adversaries can actually use. Learn how the Threat Debt Index helps security teams prioritize remediation, reduce exposure, and prove risk reduction.
    Read More